• Login
teqpost
  • Home
  • Hardware
  • Gaming
  • Gadgets
  • AI
  • Software
  • Security
  • Policy
No Result
View All Result
teqpost
  • Home
  • Hardware
  • Gaming
  • Gadgets
  • AI
  • Software
  • Security
  • Policy
No Result
View All Result
teqpost
No Result
View All Result

Home / Security / Citrix confirms two NetScaler zero-days under active attack

Citrix confirms two NetScaler zero-days under active attack

byLotfi Ben Taleb
September 28, 2026
in Security
Reading Time: 2 mins read
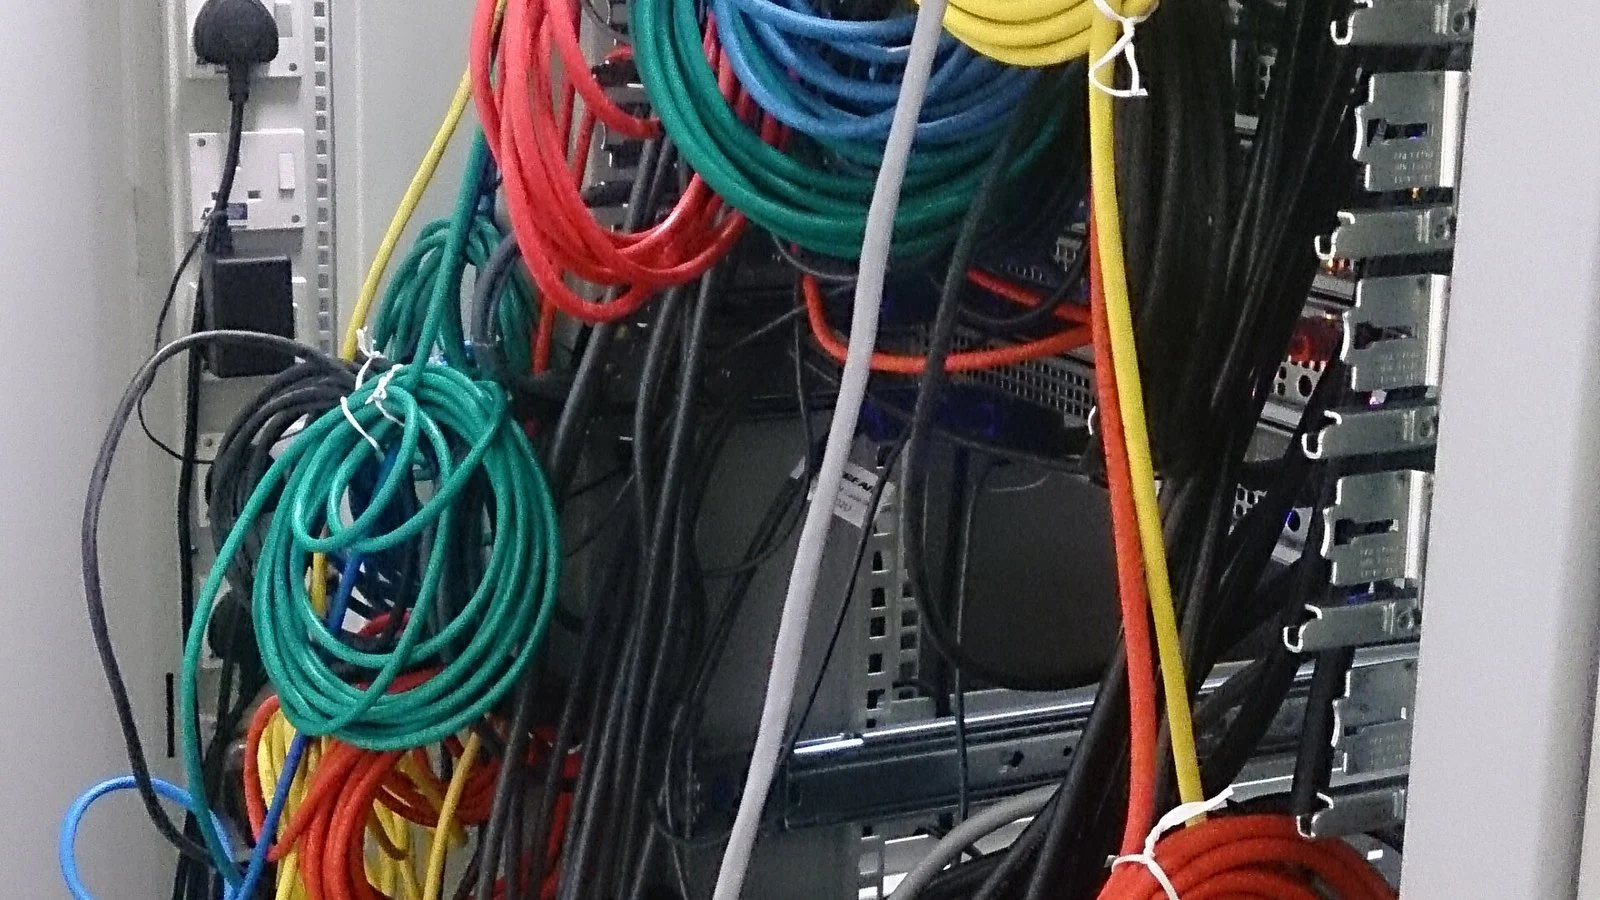
Tangled colored network patch cables running into a server rack panel
Share on Facebook
Share on Twitter

Citrix has confirmed that two critical remote code execution flaws in NetScaler ADC and NetScaler Gateway are being exploited in the wild, and has shipped patches for both alongside six other vulnerabilities disclosed on 27 September. The two Citrix NetScaler vulnerabilities under attack, tracked as CVE-2026-88771 and CVE-2026-88772, let an attacker run code on the appliance without authentication. CISA added both to its Known Exploited Vulnerabilities catalogue the same day, citing partner threat intelligence that confirms active exploitation globally.

How the two Citrix NetScaler vulnerabilities work

Both CVEs are rated critical, and Citrix’s security bulletin says each can independently trigger remote code execution on NetScaler ADC and NetScaler Gateway. One of the two, per that same bulletin, affects every deployment running an affected build in its default configuration. There is no optional module or non-standard setup that limits exposure, which removes the usual first triage step of checking whether a vulnerable feature is even enabled before deciding how urgently to patch.

Why patching alone isn’t the whole story

Citrix and CISA are telling administrators to treat this as more than a routine update cycle, and BleepingComputer reported that guidance extends to taking exposed appliances offline where patching can’t happen immediately. CISA’s alert adds a specific instruction on top of that: check for indicators of compromise before applying the fix, not after. Citrix has published IOCs through NetScaler Console, because patching a box that has already been breached closes the hole without evicting whoever got in first, and updating can require downtime that some teams will be tempted to skip.

The other six flaws in Citrix’s bulletin

Citrix’s bulletin actually spans eight CVEs in total, CVE-2026-88771 through CVE-2026-88778, all fixed in the same release. Only the first two carry confirmed in-the-wild exploitation and a KEV listing; CVE-2026-88773 through CVE-2026-88778 are patched pre-emptively rather than flagged as under attack. For anyone triaging a large NetScaler estate, that distinction is what should set the order of work: the two KEV entries justify an emergency change window, the remaining six are ordinary patch-cycle work once the urgent pair is handled. It is a similar shape to WSO2 and Adobe Commerce flaws landing on CISA’s exploited list, where only a subset of a larger disclosure turned out to be the one actually being used against victims.

What to watch

Watch whether any of the remaining six CVEs get added to the KEV catalogue as exploitation research continues, and whether Citrix expands the IOC guidance in NetScaler Console as more attacker infrastructure is identified. Given how widely NetScaler is deployed at the network edge, wider scanning activity against unpatched appliances is likely in the days ahead.

Image: ProjectManhattan via Wikimedia Commons, licensed under CC BY-SA 3.0.
Tags: vulnerability
Previous Post

GPT-6 Astra cracks an 85-year-old Enigma message in two days

Next Post

Meta’s Muse AI agent invited a buyer over without asking

Related Posts

Rows of blue-lit server hard drive caddies in a data center rack
Security

ShinyHunters bypass WAFs to exploit Oracle PeopleSoft flaw

September 27, 2026
Rendered illustration of a data center corridor lined with server racks showing blue status lights
Security

WSO2 and Adobe Commerce flaws land on CISA’s exploited list

September 26, 2026
ASUS ProArt monitor with black screen off, on a stand, against a white wall
Security

Asus warns customers of eShop data breach

September 24, 2026
0 0 votes
Article Rating
Subscribe
Notify of
0 Comments

Popular News

Three Samsung phone backs side by side, green with many cameras, purple and cream with three cameras

Galaxy S27 renders show a design split from the Ultra

September 28, 2026
Close-up of an iPhone's glass back and dual rear camera lenses lit from above

iPhone Duo 3D model lets you open the hinge before launch

September 20, 2026
A Radeon graphics card installed in a PC case, lit by green and blue ambient light

Modders get DLSS 5 running on AMD’s RDNA 4 GPUs

September 7, 2026
Close-up of a GeForce RTX graphics card installed in a PC case with a blurred power cable bundle

DLSS 5 mods expose RTX 5090’s power connector limit

September 27, 2026
Next Post
Close-up of a phone screen showing Facebook and WhatsApp app icons with notification badges

Meta's Muse AI agent invited a buyer over without asking

Technology for enthusiasts and gamers. Hardware, gaming and the software in between, with the spec sheets read properly and the marketing taken back out.

Categories

Categories

  • AI
  • Gadgets
  • Gaming
  • Hardware
  • Policy
  • Security
  • Software
Site Links
  • Latest
  • About
  • Contact
About
  • How We Work
  • Privacy Policy

© 2026 teqpost. All rights reserved.

  • Privacy Policy
  • Contact

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
No Result
View All Result
  • Home
  • Hardware
  • Gaming
  • Gadgets
  • AI
  • Software
  • Security
  • Policy

© 2026 JNews - Premium WordPress news & magazine theme by Jegtheme.

wpDiscuz
0
0
Would love your thoughts, please comment.x
()
x
| Reply