• Login
teqpost
  • Home
  • Hardware
  • Gaming
  • Gadgets
  • AI
  • Software
  • Security
  • Policy
No Result
View All Result
teqpost
  • Home
  • Hardware
  • Gaming
  • Gadgets
  • AI
  • Software
  • Security
  • Policy
No Result
View All Result
teqpost
No Result
View All Result

Home / Security / Cisco patches ISE auth bypass zero-day under attack

Cisco patches ISE auth bypass zero-day under attack

byLotfi Ben Taleb
September 18, 2026
in Security
Reading Time: 2 mins read
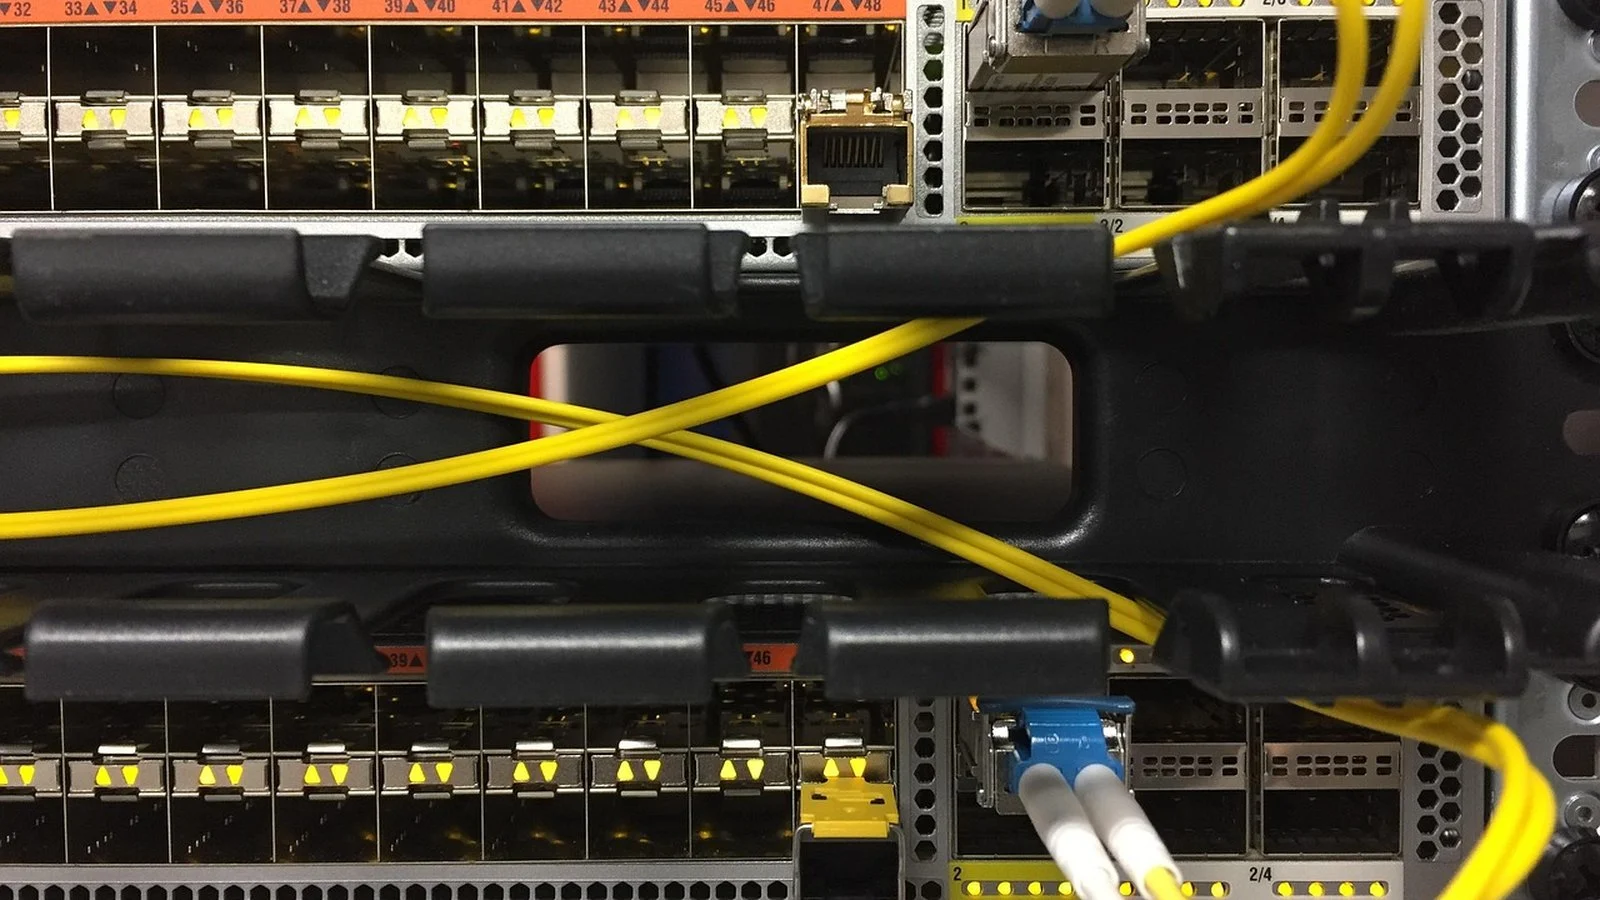
Close-up of a network switch with yellow fiber patch cables crossing between rack rails
Share on Facebook
Share on Twitter

Cisco has patched a maximum-severity flaw in Identity Services Engine (ISE) that attackers were already exploiting before a fix existed. The Cisco ISE vulnerability, tracked as CVE-2026-76460, scores a full 10.0 on the CVSS scale and lets an unauthenticated, remote attacker bypass authentication entirely. Cisco’s own advisory puts the cause plainly: insufficient authentication control on an API endpoint, which is a different failure mode from a weak check, since there is no check to weaken in the first place.

What the ISE vulnerability actually lets an attacker do

ISE is Cisco’s network access control engine: it decides which devices and users get onto a network, and under what policy, using RADIUS and 802.1X. An API endpoint that skips authentication on a platform like that is not a minor information leak, it is a door into the system that grants or denies network access in the first place. An unauthenticated attacker who reaches that endpoint does not need to steal a credential or phish an admin, they just need network reachability to the API. That is why Cisco and the CVSS scoring both treat this as a full 10.0 rather than a high-but-not-critical bypass.

Cisco’s second zero-day in three days

This is the second Cisco zero-day teqpost has covered this month. On 15 September we reported on a Secure Email Gateway zero-day that was exploited before a patch existed. That flaw sat in a different product and did not carry a perfect CVSS score. This one does, and it hit three days later, on the same underlying pattern: exploitation in the wild predates the fix, meaning any ISE deployment exposed to the internet or an untrusted segment before the patch shipped should be treated as potentially already compromised.

By our arithmetic, The Hacker News and BleepingComputer published their reports within 41 minutes of each other. That gap is too tight for one outlet to have found the flaw independently and the other to have caught up through separate reporting. It points to a coordinated disclosure: Cisco briefed press ahead of a fixed publication window, rather than reporters racing each other to a scoop. Worth knowing before treating either write-up as an independent confirmation of severity, since both are downstream of the same vendor timeline.

What to watch

Cisco has already shipped the fix, so the immediate action for anyone running ISE is patching, not waiting for more detail. What is still open is scope: Cisco’s advisory will likely be updated with the affected version list and indicators of compromise as its investigation continues, and that update is worth checking against any ISE instance that was internet-facing or exposed to an untrusted VLAN before the patch landed.
Tags: vulnerability
Previous Post

Mod unlocks 225W power target for RTX 5090 laptop GPU

Next Post

Intel reportedly prepping 8P+8E Raptor Lake Next chip

Related Posts

Tangled colored network patch cables running into a server rack panel
Security

Citrix confirms two NetScaler zero-days under active attack

September 28, 2026
Rows of blue-lit server hard drive caddies in a data center rack
Security

ShinyHunters bypass WAFs to exploit Oracle PeopleSoft flaw

September 27, 2026
Rendered illustration of a data center corridor lined with server racks showing blue status lights
Security

WSO2 and Adobe Commerce flaws land on CISA’s exploited list

September 26, 2026
0 0 votes
Article Rating
Subscribe
Notify of
0 Comments

Popular News

Three Samsung phone backs side by side, green with many cameras, purple and cream with three cameras

Galaxy S27 renders show a design split from the Ultra

October 1, 2026
Close-up of an iPhone's glass back and dual rear camera lenses lit from above

iPhone Duo 3D model lets you open the hinge before launch

September 20, 2026
A Radeon graphics card installed in a PC case, lit by green and blue ambient light

Modders get DLSS 5 running on AMD’s RDNA 4 GPUs

September 7, 2026
Close-up of a GeForce RTX graphics card installed in a PC case with a blurred power cable bundle

DLSS 5 mods expose RTX 5090’s power connector limit

September 27, 2026
Next Post
Empty CPU socket with open retention bracket on a motherboard, no processor installed

Intel reportedly prepping 8P+8E Raptor Lake Next chip

Technology for enthusiasts and gamers. Hardware, gaming and the software in between, with the spec sheets read properly and the marketing taken back out.

Categories

Categories

  • AI
  • Gadgets
  • Gaming
  • Hardware
  • Policy
  • Security
  • Software
Site Links
  • Latest
  • About
  • Contact
About
  • How We Work
  • Privacy Policy

© 2026 teqpost. All rights reserved.

  • Privacy Policy
  • Contact

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
No Result
View All Result
  • Home
  • Hardware
  • Gaming
  • Gadgets
  • AI
  • Software
  • Security
  • Policy

© 2026 JNews - Premium WordPress news & magazine theme by Jegtheme.

wpDiscuz
0
0
Would love your thoughts, please comment.x
()
x
| Reply